Resource library
Straight answers on cybersecurity. No decoder ring.
Written, recorded, and explained for people who run a business, not a security department. Pick a subject, or browse the lot.

Start where your question is.
Each subject collects everything we have written on it, so you are not piecing an answer together from six half-articles.
All SubjectsBest PracticesAIHIPAACMMCNYSDFS Part 500SOC 2Threat ResearchRansomwareGovernanceAwareness TrainingIncident ResponseThird-Party RiskVulnerability ManagementCyber InsuranceCloudManufacturingHealthcareFinancial ServicesPublic Entities
52 resources
Nothing matches that. Try a different word, or start again.
 Best PracticesShields Up: How Cybersecurity Quietly Wins You More CustomersPwC: 79% of consumers say protecting their data is what earns their trust. What that means for a smaller business, and how to show your work.
 WatchAIWhat Rogue AI Means for Smaller BusinessesA thousand days into the AI era, the "more sophisticated attacks" framing still misses the point. Watch our customer-exclusive session, now public for the first time.
 Incident Response10 Incident Response Scenarios Every Small Business Should Test Before 2027A tabletop exercise is how you find out your IR plan has gaps — before an incident does. Here are the 10 scenarios every smaller business should run through before 2027.
 NYSDFS Part 500A Risk Assessment Is Not a Document. NYSDFS Just Said So.NYSDFS issued guidance on September 10 clarifying what risk assessments under Part 500 must actually do. The exam findings list is worth reading carefully.
 RansomwareRansomware in 2027: Why the Metric Everyone's Watching Is the Wrong OneRansom payments are falling while attacks rise, and 96% of victims are smaller businesses. What the numbers actually say, and what defends against ransomware heading into 2027.
 CMMCWhat the CMMC Pause Actually Changed, and What It Didn'tCMMC Phase II is paused by binding regulation. Third-party assessments are out of contracts. But self-attestation, NIST 800-171, and False Claims Act liability are all still in effect.
 NYSDFS Part 500What NYSDFS Part 500 Compliance Looks Like in PracticeFiled your April certification. Now what? Here’s what ongoing NYSDFS Part 500 compliance looks like, and where smaller covered entities typically fall short.
 Best PracticesThe Problem with MFA (and Why You Can't Ditch It)Attackers bypassed MFA in 100% of BEC cases last quarter. That doesn't mean MFA is worthless — it means MFA alone isn't enough. Here's the honest read.
 GovernanceEffective Governance for Smaller BusinessesGovernance is the most-skipped part of cybersecurity. Here’s what frameworks, policies, and plans actually mean for smaller businesses, and why they matter.
 AIAI at OrbitalFire: Our Strategy, Policy & RobotsA look inside OrbitalFire's AI strategy — how we use "robots," our open-source AI acceptable use policy, and the new AI Readiness Assessment.
 GovernanceCybersecurity Resilience: Why Compliance Isn’t EnoughPassing compliance checks doesn’t mean your business is secure. Learn why cybersecurity resilience determines whether your organization survives an incident.
 Awareness TrainingWhy Security Awareness Training Fails (and What Works Instead)Most employees know what phishing is — and still click. Here’s how smaller organizations build security culture with awareness training that changes behavior.
 Incident ResponseIncident Response in 2026: How Small Businesses Should PrepareA plan nobody has practiced is a document, not preparation. What a workable incident response plan contains, and how a tabletop exercise changes behavior.
 Vulnerability ManagementWatch: 7 Vulnerability Management Tips for Small BusinessesLearn 7 vulnerability management tips every small business needs to reduce cyber risk. Discover how to spot gaps, prioritize fixes, and stay ahead of attackers.
 SOC 2Mission SOC 2: Practical Readiness for Smaller BusinessesSOC 2 compliance is showing up in more vendor contracts. Here's what it actually means, who needs it, and how smaller businesses can realistically get there
 Cyber InsuranceCyber Insurance for Smaller BusinessesIn this article, OrbitalFire breaks down what cyber insurance really covers, when it makes sense, common pitfalls, and how to make it work for small businesses.
 AIAI Scams & Deepfakes: A New Frontier of Small Business FraudCloned voices and faked video are being used against businesses too small to expect it. How the scams work, and the habits that stop a convincing one.
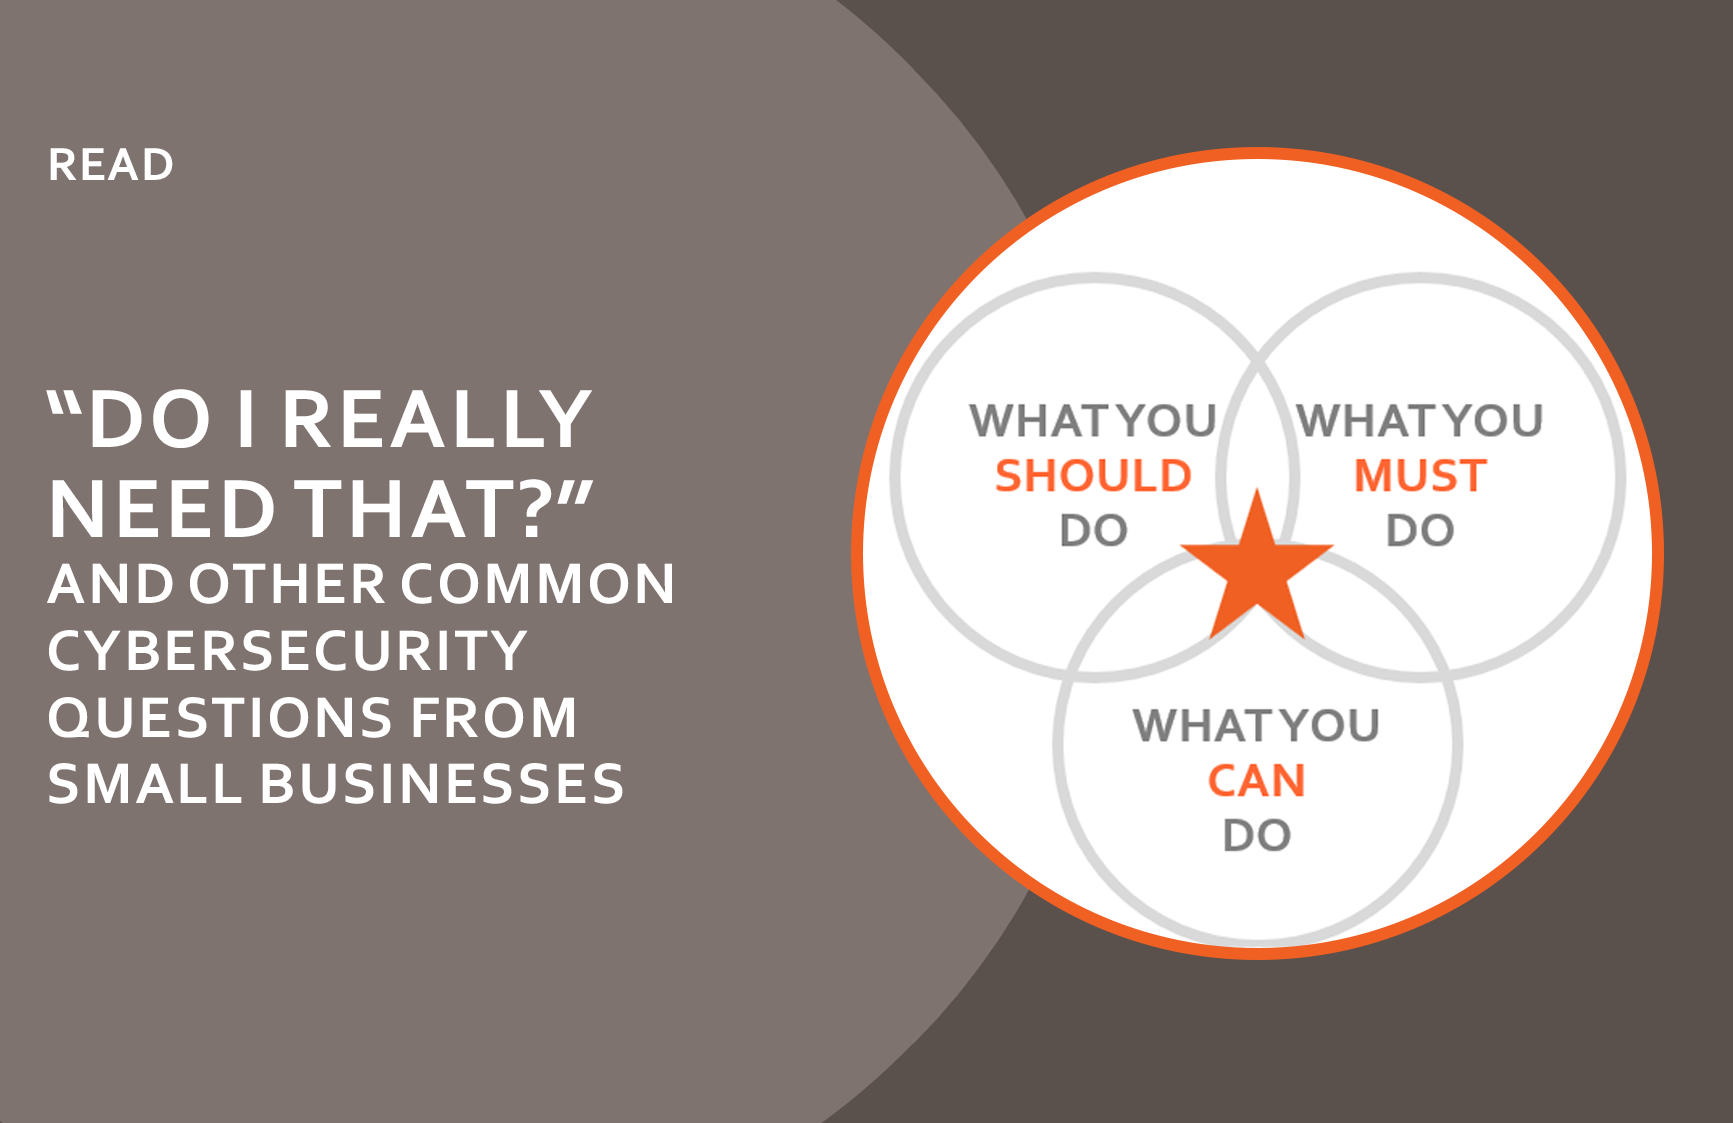 Best PracticesTop Cybersecurity Questions from Small BusinessesThis article discusses some of the most common cybersecurity questions we hear at OrbitalFire and perspectives small businesses should consider.
 AIAI and Small Business Cybersecurity: Hype vs. RealityAI is reshaping cybersecurity for both defenders and attackers. For small businesses, AI won’t save you, but it can help you if you know how to use it.
 Awareness TrainingREAD: The 'GAUGES' Method of Spotting a PhishProtect sensitive company and customer data from potential cyber threats. Use the OrbitalFire ‘GAUGES’ method to detect phishing and social engineering scams.
 CloudWhat Small Businesses Need to Know About Cloud ComputingYour data is on somebody else’s computer. The questions worth asking about who can reach it, what the provider is responsible for, and what stays yours.
 CloudWATCH: A Security Forecast for Cloud ComputingCloud computing is fast, scalable, and full of security risks most small businesses don't know to look for. Here's how to stay protected when your data lives somewhere else.
 Incident ResponseCrisis-Proof Your Organization with an Incident Response PlanCyber attacks are surging in both frequency and sophistication. Without an incident response plan, the aftermath can lead to financial losses and more.
 ManufacturingWatch: Cybersecurity Crash Course for Small ManufacturersManufacturing is now one of the most targeted industries for cyberattacks. Here's what smaller manufacturers need to know that most cybersecurity guides skip.
 Third-Party RiskManaging Third Party Cybersecurity Risk WebinarThird-party vendors are one of the most common entry points for cyberattacks on smaller businesses. Here's how to know who has access and limit the risk.
 Cyber InsuranceCyber Insurance: What Every Small Business Should KnowCyber insurance is harder to qualify for, easier to have denied, and more important than ever. Here's what smaller businesses need to know before their next renewal.
 HIPAAThe HIPAA Security Rule Hasn't Changed in 20 Years.The new HIPAA Security Rule is now expected July 2027, but the five major changes are coming. OrbitalFire and Kurt Bratten break down what healthcare orgs need to know now.
 ManufacturingThe ISO 9001 Gap Nobody's Talking AboutISO 9001 is getting an update, and cybersecurity should be part of your readiness plan. Here's what manufacturers need to know about the gap in QMS programs.
 WatchHIPAAHIPAA Security 2.0: What to Expect from the Impending Update
 WatchGovernancePolicies, Plans, and Frameworks: Effective Governance for Smaller Businesses
 AIAI-Powered Cyber Threats: What New Research Means for Small BusinessNew research from Anthropic shows AI nearly doubled the share of dangerous hackers in one year. Here's what smaller businesses need to know, and do.
 Best PracticesOut of Office, Open Season: Summer Cybersecurity TipsSummer cybersecurity for smaller businesses isn't just about airport Wi-Fi — it's about what happens when half the team is OOO. Here's the playbook.
 Threat Research2025 FBI IC3 Report: What Smaller Businesses Need to KnowThe 2025 FBI IC3 Report shows $20.9B in cybercrime losses and a new AI section. Here's what smaller businesses should actually do about it.
 HIPAAHIPAA Security Rule Update 2026: What Your Organization Should KnowThe first HIPAA Security Rule update in 20 years changes how covered entities verify vendor compliance — and what healthcare organizations need to do now.
 WatchAIAI at OrbitalFire: An Inside Look at Our Strategy
 Third-Party RiskWhen Your Vendors Drop the Ball, Who Pays? You Might Be Surprised.A $500K ransomware case shows what happens when vendors don't deliver on security. Here's what smaller businesses need to know about vendor cybersecurity accountability.
 ManufacturingCybersecurity for Small Manufacturers is a Competitive AdvantageCybersecurity is a competitive advantage. Learn how getting ahead of cyber risk wins contracts, builds trust, and drives growth.
 GovernanceYour HR Team Is a Cybersecurity Asset: How to Leverage ThemYour HR team already owns onboarding, offboarding, and policy enforcement: your biggest cyber exposures. Here's how to make cybersecurity and HR work together.
 Public EntitiesNY Wastewater Cybersecurity Regulations: What Public Entities Need to KnowNew York’s new DEC wastewater cybersecurity regulations are now in effect. Learn about incident reporting, compliance dates, and operational requirements.
 GovernanceInsider Threat in Small Business: The Advantage You HaveMost insider incidents are not sabotage — they are access nobody revoked. Why smaller businesses spot the signals sooner, and what to do about offboarding.
 HealthcareHealthcare Cybersecurity and Resiliency Act of 2025What is the Healthcare Cybersecurity and Resiliency Act of 2025, and how does it relate to HIPAA? Learn what smaller healthcare providers should do now.
 Best PracticesWhat Cybersecurity Resolutions for Small Businesses Work?Learn which cybersecurity resolutions for small businesses for work, and how to build habits that reduce real risk, not just check boxes.
 WatchVulnerability ManagementMind the Gaps: 7 Vulnerability Management Tips for Small Businesses
 Best PracticesCybersecurity Steps Small Businesses Should Take Before 2026Six things worth doing before the year closes — people, process, and planning, not firewalls. The areas that decide how a small business handles an incident.
 CMMCREAD: CMMC Readiness Countdown: Don’t Panic, Get PracticalWhat matters for CMMC readiness is how well you can demonstrate your compliance. Read our practical guide to getting started with, and through certification.
 Third-Party RiskThird-Party Risk: It Could Be Your Biggest Cybersecurity ThreatManaging Third-Party Risk in cybersecurity isn’t about building a fortress around your business, it’s about building smarter fences. Read More to get started
 Best PracticesCybersecurity Time Machine: What Small Businesses Will Face in 2030Cybersecurity isn’t static. The threats we’re preparing for today are only warming up. Read to learn what small businesses can expect for cybersecurity by 2030.
 Best PracticesREAD: The Cybersecurity Zodiac: What’s Your Risk Sign?Astrology might not be NIST or HIPAA-approved, but there are definite cybersecurity risk personalities in the small business universe. Find your sign.
 Best Practices5 Cybersecurity Tasks Your SMB Should Tackle This SpringDuring this year's spring cleaning, don’t forget your digital house. Here are five cybersecurity tasks that will leave your systems feeling a whole lot safer.
 RansomwareA Small Business Guide to Ransomware DefenseRansomware is one of the fastest-growing threats to small businesses like yours. Here’s how to build resilience against ransomware and keep your business safe.
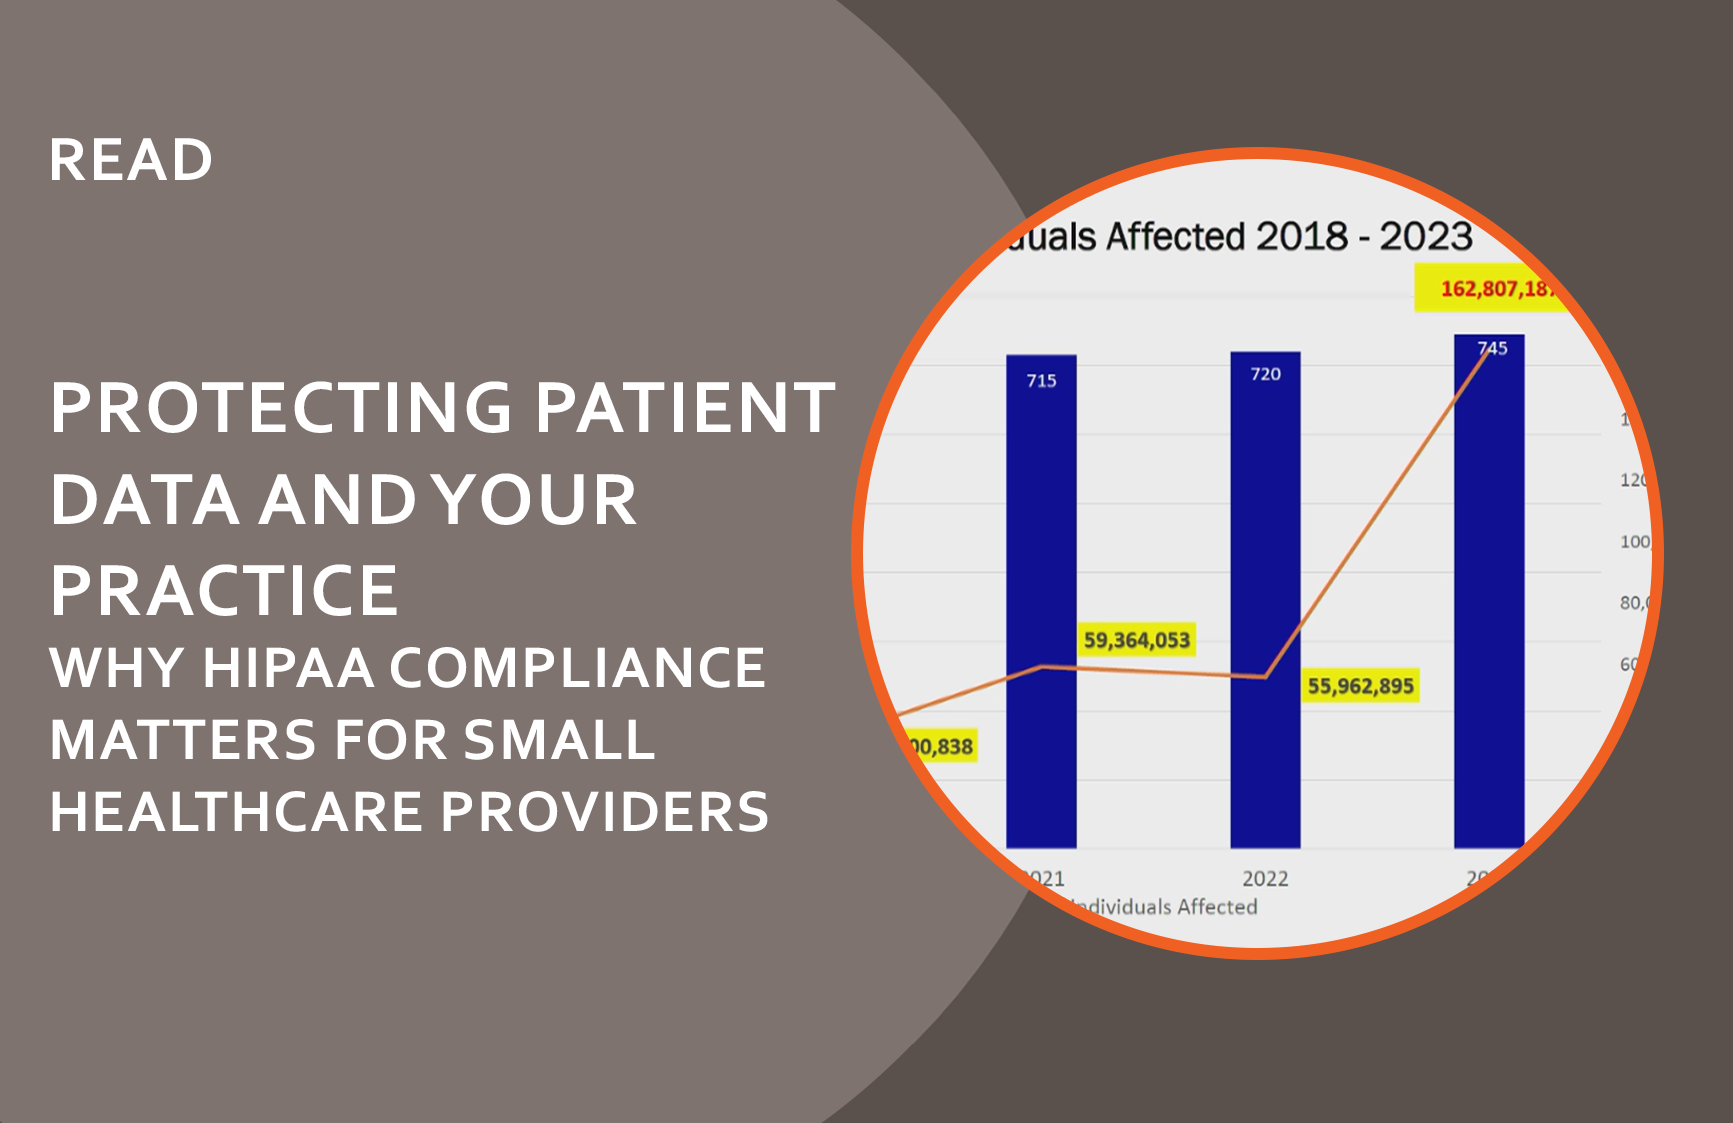 HIPAAProtecting Patient Data: Why HIPAA Compliance MattersFor small healthcare providers, maintaining HIPAA compliance is no small task. Recent data shows the risks of falling behind are greater than ever. Learn More
 NYSDFS Part 500READ: NYSDFS Amendment Upcoming Deadlines for Covered EntitiesThe NYSDFS Amendment deadlines that have landed, which ones apply to a smaller covered entity, and what the annual certification actually asks for.
 Third-Party RiskREAD: Increase in Third-Party Incidents Impacting Small BusinessesWe are aware of several customers being directly impacted by recent third-party incidents. We outline what you should do immediately to protect your business.
 Best PracticesListen: I'm in with the ARCC on Small Business CybersecurityListen to Reg Harnish, CEO of OrbitalFire discusses cybersecurity priorities for small businesses, including important first steps on I'm in with the ARCC.
 GovernanceIt's Time to Commit to a Cybersecurity StrategyAlthough a cybersecurity strategy might not have as much allure as a six-pack (depending on who you ask), it’s crucial for your business's well-being.
 WatchCMMCCMMC Final Rule Will Show Up in Contracts by October
 Vulnerability ManagementWhy We Built Our Own Configuration BenchmarkThe CIS Benchmarks run to thousands of rules written for enterprises with a security team. The OrbitalFire Configuration Benchmark is the version a smaller business can actually hold to, mapped to HIPAA, NIST 800-171, NYSDFS, and SOC 2.
 WatchAwareness TrainingBeyond Awareness Training: Advanced Tips for Securing Your Humans
 WatchCloudCloudy with a Chance of Awesome: A Security Forecast for Cloud Computing
 WatchCyber InsurancePutting the Cyber in Cyber Insurance
 WatchThird-Party RiskGood Fences Make Good Neighbors: Managing Third Party Risk
 WatchVulnerability ManagementPenetration Testing for Small Businesses
 WatchBest PracticesSize Matters: Small Business Cybersecurity
 WatchBest PracticesOrbitalFire: Keeping Up with the Cybersecurity Mandates
 WatchNYSDFS Part 500NYSDFS Cybersecurity Amendment: What You Need to Know
 WatchAIThe Future of AI in Cybersecurity
 WatchManufacturingCybersecurity for Manufacturing
 WatchVulnerability ManagementPenetration Testing for Small Business
 WatchFinancial ServicesSecuring Financial Transactions
 WatchIncident ResponseCybersecurity Incident Response
 WatchGovernance5 Reasons MSPs Need a Cybersecurity Partner
 WatchBest PracticesCybersecurity Lessons from the Coronavirus
 WatchBest PracticesSmall Business Cybersecurity: It’s All About the Data